
Salesforce integration governance for partner teams is the set of decisions, controls, and working agreements that keep connected systems reliable when both your employees and outside providers make changes. It gives everyone a clear answer to a practical question: who can change what, how is that change reviewed, and who responds if it fails? Without those answers, even a sound integration can become difficult to maintain.
Discuss your Salesforce integration needs
What does integration governance cover?
Integration governance is not a committee that approves every technical detail. It is a lightweight operating model for decisions that can affect data, business processes, security, or service continuity. It makes the boundaries between your organization, the Salesforce team, and each integration partner explicit.
A useful model covers at least five areas: ownership, design standards, access and security, release management, and ongoing support. The exact controls should match the impact and complexity of the connected process. A feed that updates a low-risk reference field does not need the same approval path as a connection that creates financial transactions or updates customer records.
Governance also makes partner work easier to evaluate. A provider can build within a shared set of rules rather than relying on assumptions. Your team retains a clear view of decisions and can support the solution after a project ends. This is especially important when several providers, internal administrators, and system owners work in the same Salesforce environment.
Which systems and processes need an owner?
Start with a current integration inventory. Do not limit the list to custom APIs. Include middleware, scheduled file transfers, marketplace applications, web forms, data loads, and manual workarounds that move information between systems. The inventory should show what each connection does, not only what technology it uses.
For each integration, record the business process, source and destination, data exchanged, direction of flow, timing, technical method, and business impact if it stops. Add the system owner and the person or team responsible for technical support. If a vendor operates a platform or connector, identify that relationship as well. Note whether the integration is active, being replaced, or no longer understood.
Then assign one accountable business owner for the process. Technical teams may share delivery responsibilities, but there should be one person who can explain why the connection exists, which outcomes matter, and what should happen when the business process changes. A named owner prevents a common gap: everyone knows the connection is important, yet no one is authorized to make a decision about it.
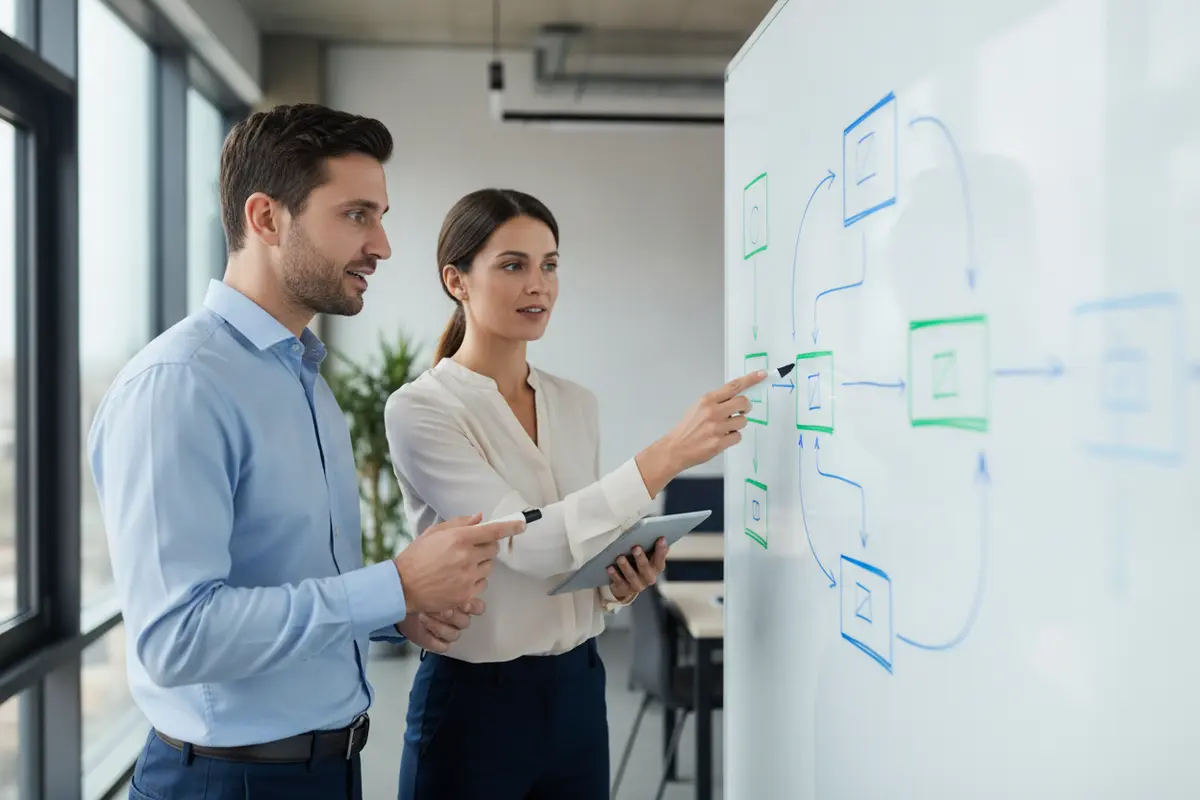
Keep the inventory useful rather than perfect. A spreadsheet or a maintained diagram can be enough at first if it is accessible, current, and linked to the delivery and support process. For a broader view of how an implementation can be broken into manageable work, see this guide to Salesforce implementation phases.
How should decision rights be divided?
Write down who recommends, approves, implements, and supports each meaningful change. In a small team, one person may hold several roles. The important point is that the roles are visible and conflicts are handled before a change is urgent.
Business process owner: Confirms the need, business rules, acceptable impact, and priority. Salesforce owner: Assesses effects on Salesforce configuration, data, users, and other automations. Source-system owner: Confirms upstream data definitions, availability, and change plans. Integration lead or partner: Designs and implements the agreed technical change, documents it, and supports testing. Security or compliance reviewer: Reviews access, sensitive data, retention, and applicable internal controls. Release owner: Coordinates deployment timing, approvals, rollback planning, and communication.
A responsibility matrix can clarify handoffs, but do not let a matrix replace a real decision path. For example, specify who can approve a new field being sent to another platform, who accepts a change to a production schedule, and who can pause a release when testing reveals a problem. Escalation should have a named route and a reasonable response expectation.
Partners should be included in the governance process, not treated as owners of your business decisions. They can advise on options and explain technical consequences. Your organization should retain authority over business rules, data use, risk tolerance, and priorities. This preserves control while giving the delivery team enough room to work efficiently.
What standards should integration partners follow?
Agree on design and documentation standards before multiple projects create competing patterns. These standards do not need to dictate a single technology for every use case. They should define what a solution must demonstrate and what information the team must leave behind.
Specify how integrations are named, where configuration and credentials are managed, how errors are recorded, how retries work, and how duplicate or out-of-order messages are handled. Decide how teams identify the system of record for each important data element. Document the expected behavior when a source system is unavailable or sends incomplete data. These details turn general expectations such as “make it resilient” into reviewable design choices.
Set documentation expectations too. For each connection, keep a diagram, data mapping, field-level rules where needed, dependencies, schedules, contacts, test evidence, and support instructions. Record assumptions and decisions, including rejected alternatives when they could come up again. Documentation should be stored in a location your organization controls and should be understandable to someone who did not build the integration.
Ask partners to use the standards in their proposals and design reviews. If an exception is justified, record what is different, why it is necessary, what risk it creates, and who accepted that risk. A documented exception is easier to revisit than an undocumented variation that becomes the de facto standard.
How can access and data risk be controlled?
Use the least access needed for each person, service account, and connected application. Separate individual access from non-human integration access. Establish who requests, approves, provisions, reviews, and removes access, including when a partner engagement changes or ends.
Before sharing data, identify which fields and records the process actually needs. Confirm the business purpose, direction of movement, and permitted use. Consider whether the destination needs a full record or only selected fields. Limit access to sensitive information and use the controls available in the systems involved. Your security, privacy, and compliance owners should determine the applicable rules for your organization; a delivery partner should not guess those requirements.
Agree how credentials and secrets will be protected and rotated, and how access will be revoked. Avoid making a single consultant's personal account the only way an integration operates. Confirm what activity is logged, who reviews alerts, and how potential exposure is escalated. For partners, set expectations for secure work practices and ensure that access is limited to the period and scope of the engagement.
These checks should happen during design, not as a final hurdle just before launch. If the review discovers a data concern late, teams may face pressure to accept a shortcut because development is already complete. Early review leaves room to adjust the data flow or process design before the choice becomes expensive to change.
How should teams manage releases and changes?
Every integration change needs a clear path from request to production. The path can be lightweight for a low-impact adjustment, but it should still capture the reason for the change, affected systems, owner, testing, approval, and release window. Changes made by a partner should follow the same controls as changes made by employees.
- Log the request. State the business need, expected result, urgency, and affected process.
- Assess the impact. Identify connected systems, data, users, dependencies, and possible failure effects.
- Approve the design. Confirm the business rule, technical approach, access implications, and accountable owners.
- Build and test. Use representative scenarios, including invalid data, duplicates, delays, and recovery where relevant.
- Plan the release. Define timing, communications, monitoring, rollback or workaround steps, and the person authorized to act.
- Review after release. Confirm the intended result, close outstanding issues, and update the inventory and support documentation.
Testing should reflect the real process, not only whether two systems exchange a sample record. Include expected volumes and timing when they matter, exception handling, permissions, and downstream effects. Have business users confirm that records and workflows behave as intended. The partner can provide test evidence, but the business owner should accept the business outcome.
Define an emergency path for an urgent defect, too. State who can authorize a limited change, how the risk is recorded, and when the normal review and documentation must be completed. An emergency process should make fast action possible without making undocumented production changes routine.
What should ongoing support and monitoring include?
Agree on what “working” means for each integration. It may include successful processing, expected freshness of data, acceptable error rates, or completion before a business deadline. Choose measures that connect to the process. A green technical status is not enough if important records are delayed or users are repeating work manually.
Document how failures are detected and who receives alerts. Specify who triages the issue, who can contact the other system's provider, and who communicates with affected users. Decide how the team handles retries, failed messages, data correction, and reconciliation. A connection can recover technically while leaving a business process with missing or duplicated records, so recovery needs a business check as well.
Set support expectations in the working agreement: coverage hours, response and escalation paths, access during incidents, evidence to collect, and the boundary between project work and ongoing support. Avoid promising a response level that the parties have not agreed and resourced. If your organization uses a managed service or an internal team, write down how responsibilities transfer between them.
Review performance and recurring incidents at a regular cadence. Repeated manual corrections may indicate a data mapping problem, a process mismatch, or a control that is too weak. An integration that rarely fails may still need attention when a system, business rule, or data owner changes. Governance should trigger review when the context changes, not only after a visible outage.
How do you compare partner delivery approaches?
Evaluate proposed approaches against the same business scenario. Ask each provider to show how ownership, design decisions, testing, deployment, and support would work in practice. The comparison below is a discussion aid, not a ranking. The best fit depends on the number of systems, internal capacity, risk, and how much knowledge your team needs to retain.
| Delivery approach | Where it can fit | Governance questions to ask | Trade-off to examine |
|---|---|---|---|
| Internal team-led | Your team has the capacity and skills to design, build, and support the connections. | Who covers specialist gaps, reviews architecture, and manages support during absences? | Strong direct control, but workload and expertise may be constrained. |
| Partner-led project | You need defined integration work or a time-bound implementation. | Who approves business rules, owns access, accepts tests, and receives complete handover? | Brings delivery capacity, but continuity depends on documentation and transfer. |
| Augmented team | Your staff lead the work and need additional capability or capacity. | Which decisions remain internal, and how are partner staff included in controls? | Can extend the team, but unclear authority can create duplicated work. |
| Ongoing managed support | You need continuing monitoring, maintenance, or optimization after launch. | What is in scope, how are incidents escalated, and how does ownership remain visible? | Provides a continuing support path, but scope and handoffs must be explicit. |
When you review a statement of work, connect each deliverable to an acceptance method and a named approver. Include integration inventory updates, architecture and mapping documents, test evidence, deployment notes, and knowledge transfer where needed. For questions that extend beyond integration delivery, this overview of Salesforce consulting services can help frame the broader engagement.
Also ask how the provider will work with your existing administrators and system owners. A technically capable partner may still struggle if it cannot get timely answers about business rules or dependencies. Conversely, an internal team may need a partner to challenge assumptions and make complex trade-offs clear. The proposal should show a collaboration model, not simply a list of technical tasks.
What belongs in a partner governance scorecard?
A scorecard helps buyers compare evidence instead of relying on broad promises. Use a consistent scale, such as not addressed, partially addressed, or clearly defined with an owner and proof. Ask for examples from the proposed approach, not confidential details from another customer.
Ownership: Are business, system, technical, security, and support owners identified? Design: Are data flow, failure behavior, dependencies, and exceptions explained? Controls: Are access, change approval, testing, and release responsibilities clear? Operations: Are monitoring, triage, recovery, and escalation covered? Handover: Will your organization receive current documentation and the knowledge to operate the work? Outcome: Is the business result defined, with a way to verify it after release?
Ask the partner to identify decisions it needs from you and the point at which each decision is required. This exposes dependencies early. It also helps you distinguish a sound proposal from one that assumes access to undocumented systems, rapid approvals, or data definitions that nobody has confirmed.
Use the same review to assess your own readiness. If no one can explain who owns a source system, a partner cannot reliably settle that question for you. Assign an internal owner or make the unresolved issue an explicit discovery task. A good evaluation surfaces these gaps before they become build delays.
Which warning signs deserve a closer look?
Be cautious when a proposal treats integrations as a collection of connectors without explaining the business process they support. Another warning sign is a design with no named owner for data quality, approvals, or production incidents. A partner should be able to describe failure handling in plain language, not only present a diagram of the successful path.
Ask follow-up questions if the plan depends on a single person's credentials, skips testing with real business scenarios, leaves no time for handover, or assumes that the source and destination always agree. Also look for vague acceptance criteria such as “integration complete” with no account of which records, events, exceptions, and users will be verified.
These signals do not automatically disqualify a provider. They may reflect missing information that can be resolved in discovery or in the contract. The important distinction is whether the provider recognizes the risk and proposes a practical way to close it, or dismisses governance as unnecessary overhead.
How can you keep governance proportionate?
Use risk to decide where review is deeper. Consider the sensitivity and volume of data, the number of systems, process criticality, recovery options, and the consequences of an error. A low-impact connection with a clear owner can use a brief review and simple tests. A connection that affects customer service, financial workflows, or critical operations deserves more explicit design review, access checks, test evidence, and recovery planning.
Start with a small set of shared artifacts: an integration inventory, a decision and ownership record, a change path, and a support handoff. Reuse them rather than creating a new form for each partner. Review the set when you add a system, change a business process, change providers, or discover a recurring incident. Governance is useful when it helps people make decisions, not when it becomes paperwork with no operational purpose.
Measure outcomes at both the technical and business levels. Technical indicators can show processing success, errors, and freshness. Business checks can show whether the intended workflow is completed, whether staff still need manual workarounds, and whether records need correction. Agree on a starting point and review period before work begins so that the team can tell whether a change improved the process.
For example, if an integration is intended to reduce rekeying, verify whether the relevant steps are actually removed and whether exceptions remain manageable. If the aim is more timely information, confirm that users receive the information when they need it. Do not treat a successful deployment as proof of business value; follow up after the process has had time to run.
Teams planning a broader Salesforce roadmap can also review Salesforce expertise and capabilities, the practical guidance on Salesforce integration services, and the guide to defining a Salesforce implementation scope of work. If data movement is a major concern, review the related Salesforce data migration practices as a separate workstream.
Talk through your integration governance plan
Frequently asked questions
Who should own a Salesforce integration?
Assign a business owner who is accountable for the process and its intended result. Technical responsibility can be shared among Salesforce administrators, system owners, and a delivery partner, but one person should be able to prioritize business needs and accept the outcome.
Does every integration change need formal approval?
Every change should have an appropriate review, but the depth can vary with risk. A routine low-impact adjustment may use a streamlined path. Changes that affect sensitive data, important workflows, access, or several systems need more deliberate review and documented acceptance.
What documentation should a partner hand over?
At minimum, request an updated integration inventory entry, design or flow diagram, relevant data mappings, dependencies, error and recovery guidance, test evidence, release notes, and support contacts. Keep the materials in a location your organization controls and make sure the internal owners can use them.
How often should integration governance be reviewed?
Review it when systems, partners, data rules, or business processes change, and after recurring incidents. A regular operational review can also identify stale documentation and emerging support needs. The right cadence depends on how critical and changeable the integrations are.
When ownership, review paths, and support responsibilities are clear, partners can make changes with less uncertainty and your team can retain control of the decisions that matter. Start with the integrations that carry the greatest business impact, then extend the same practical approach as your Salesforce environment grows.